Watchtower
A better AWS Security Hub console in your own AWS account: fast search, a fix list with Terraform and CloudFormation, tasks, exceptions and findings mapped to your code.
[ P ] LATEST POSTS
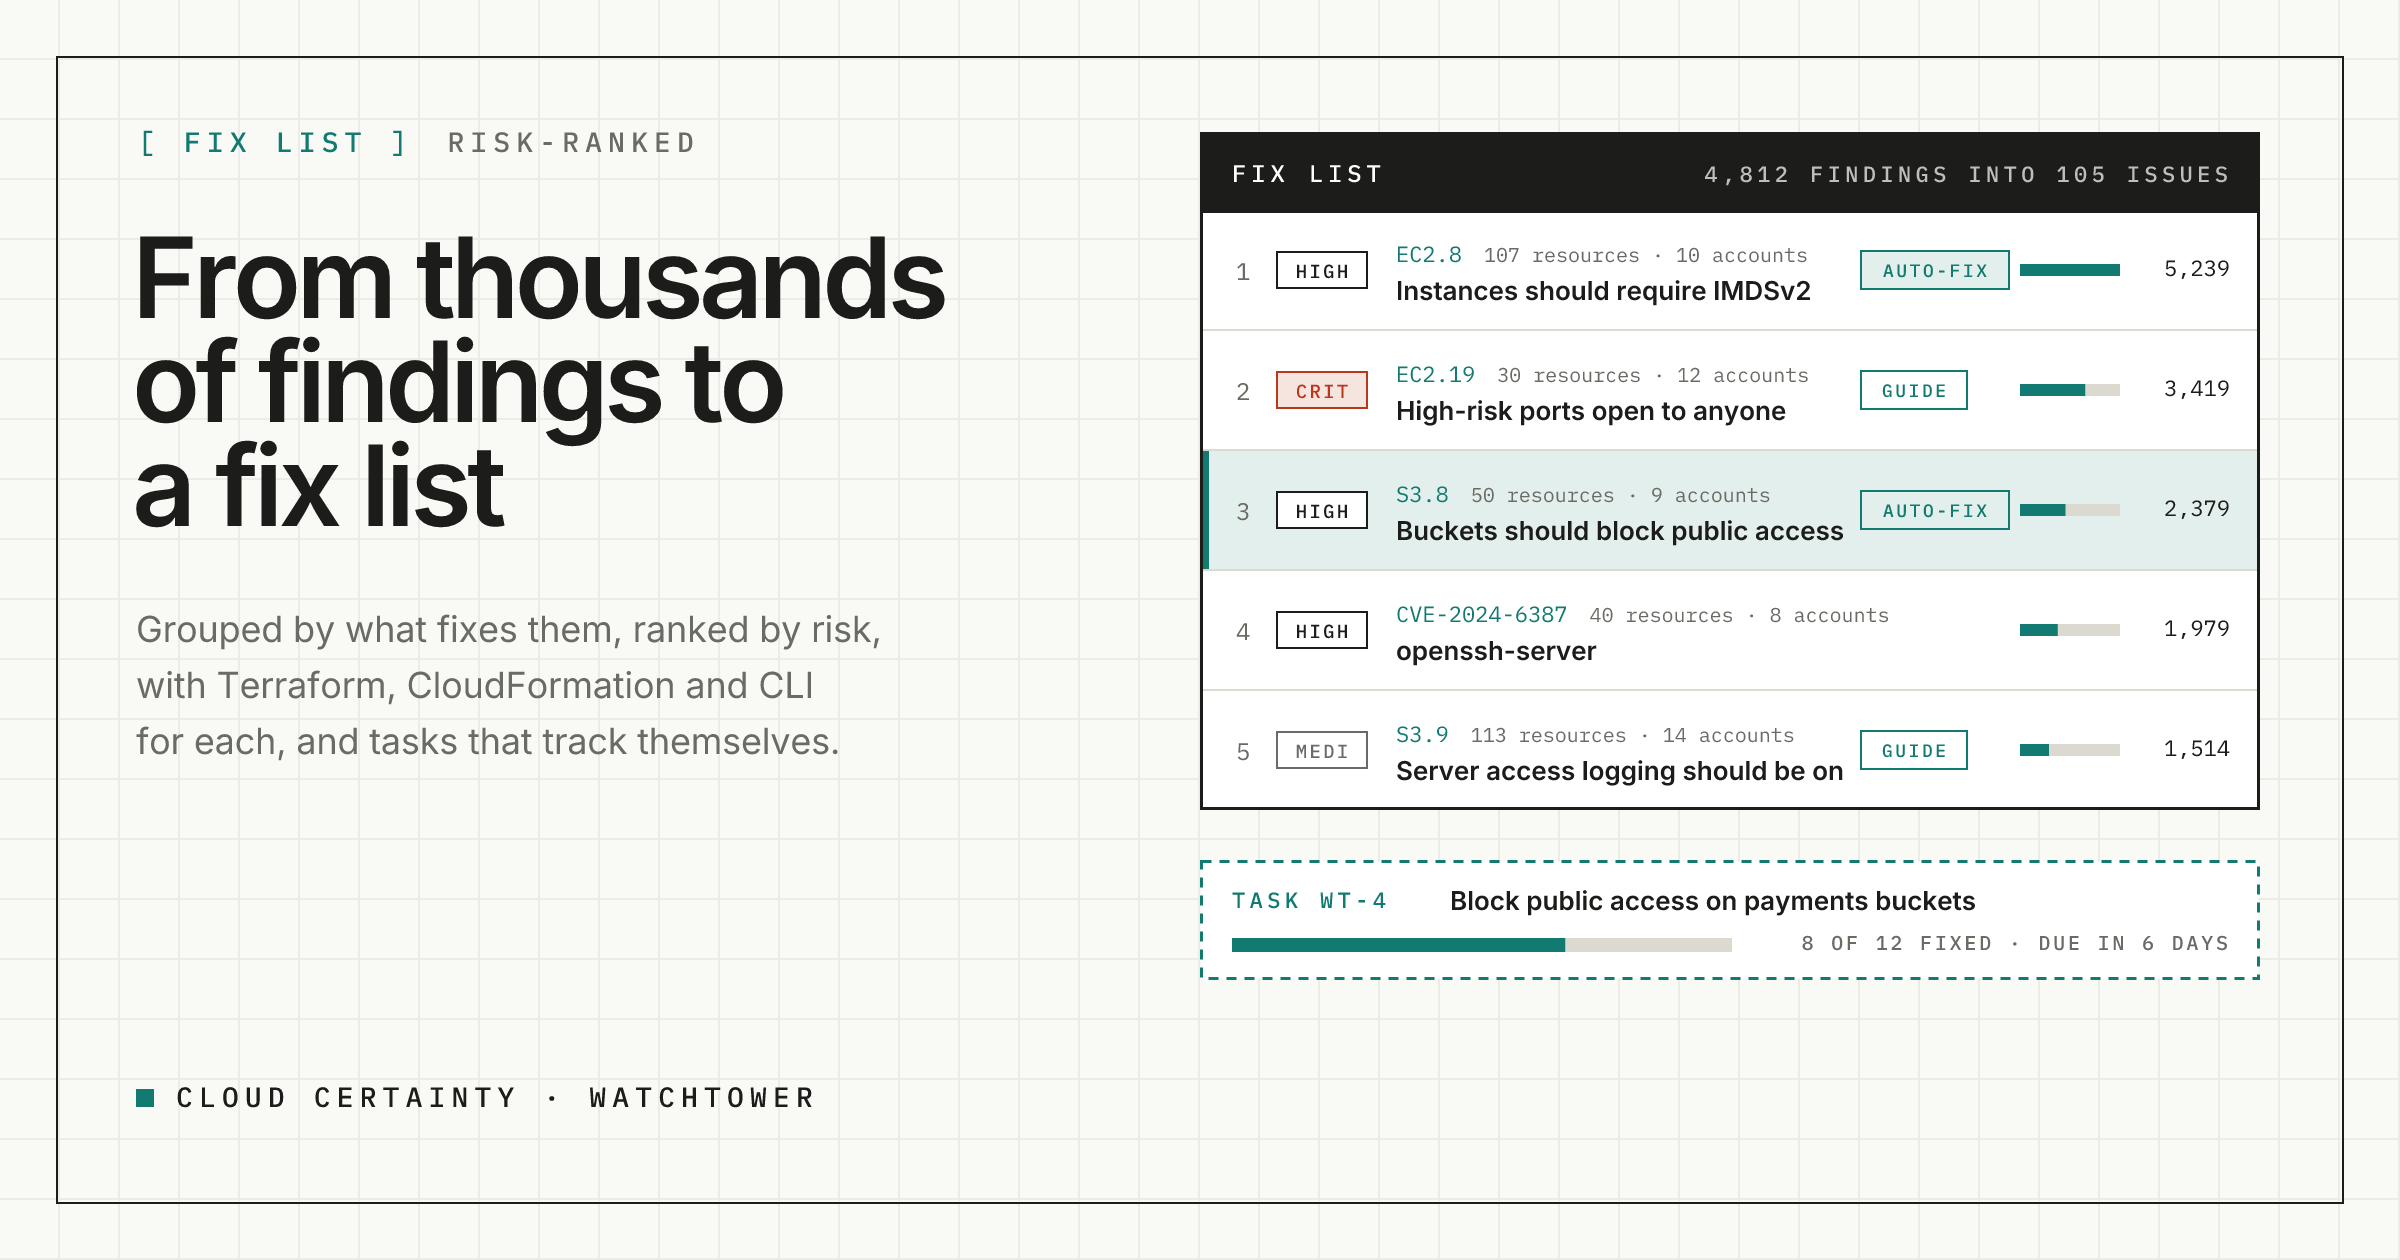
From thousands of Security Hub findings to a fix list
Most open Security Hub findings are the same few problems on many resources. Here is how Watchtower groups them by what fixes them, ranks them by risk, and keeps the work moving with tasks, SLAs and exceptions that expire.
4 min read →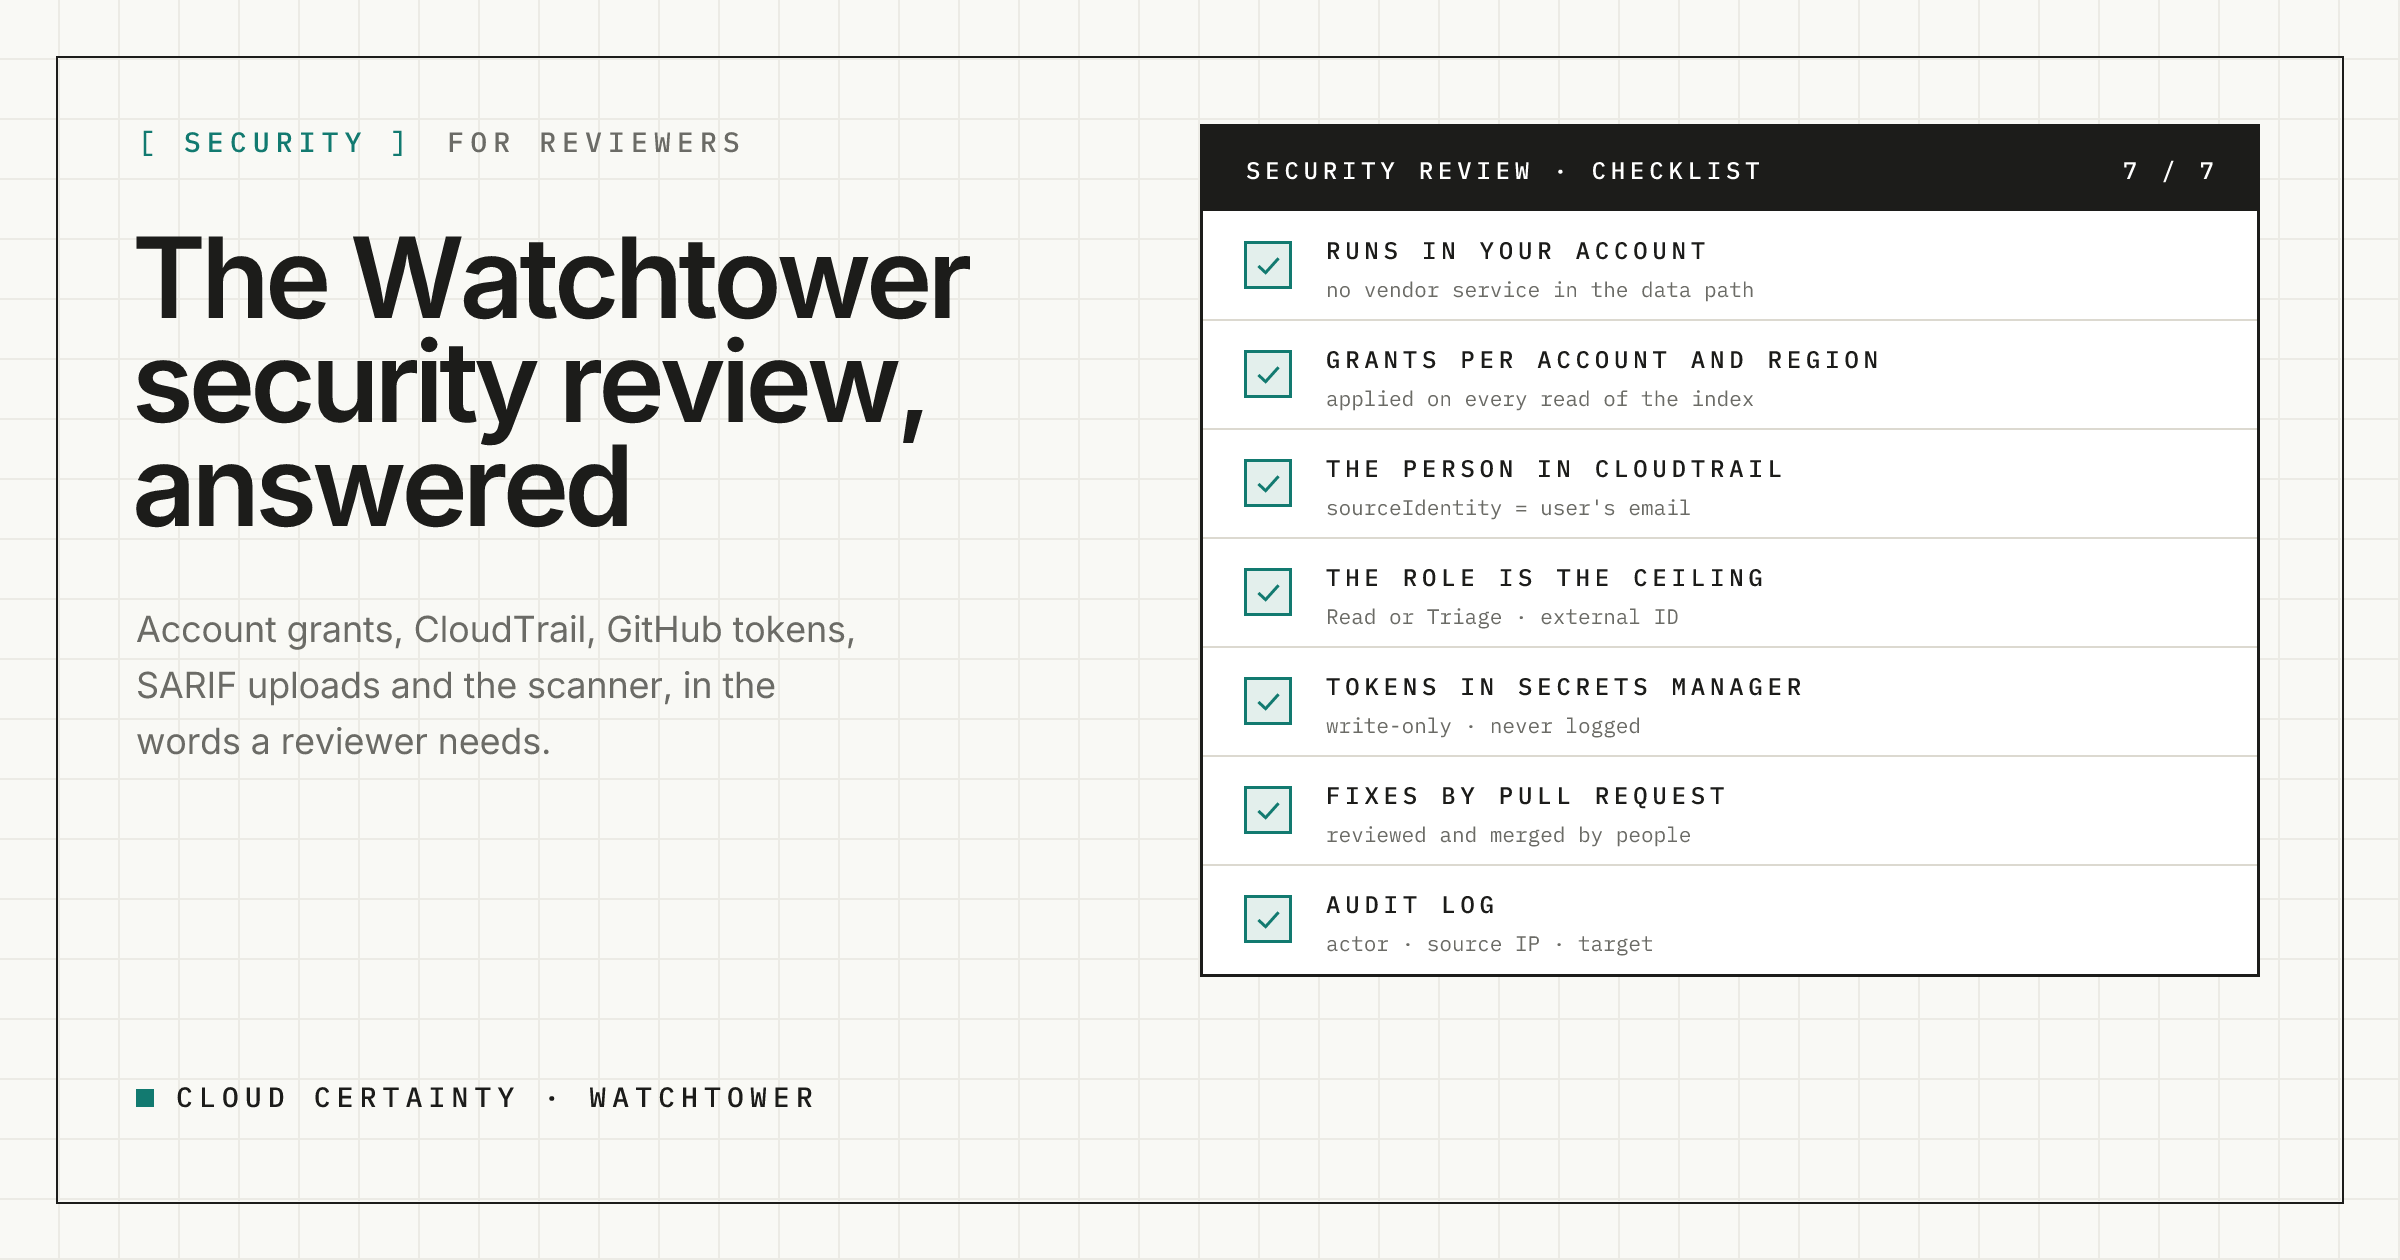
The Watchtower security review: answers to the questions reviewers ask
A tool that reads every finding in your organisation and can open pull requests on your infrastructure code has to pass a security review. These are the questions reviewers ask about Watchtower, answered with what it does and what is left to you.
5 min read →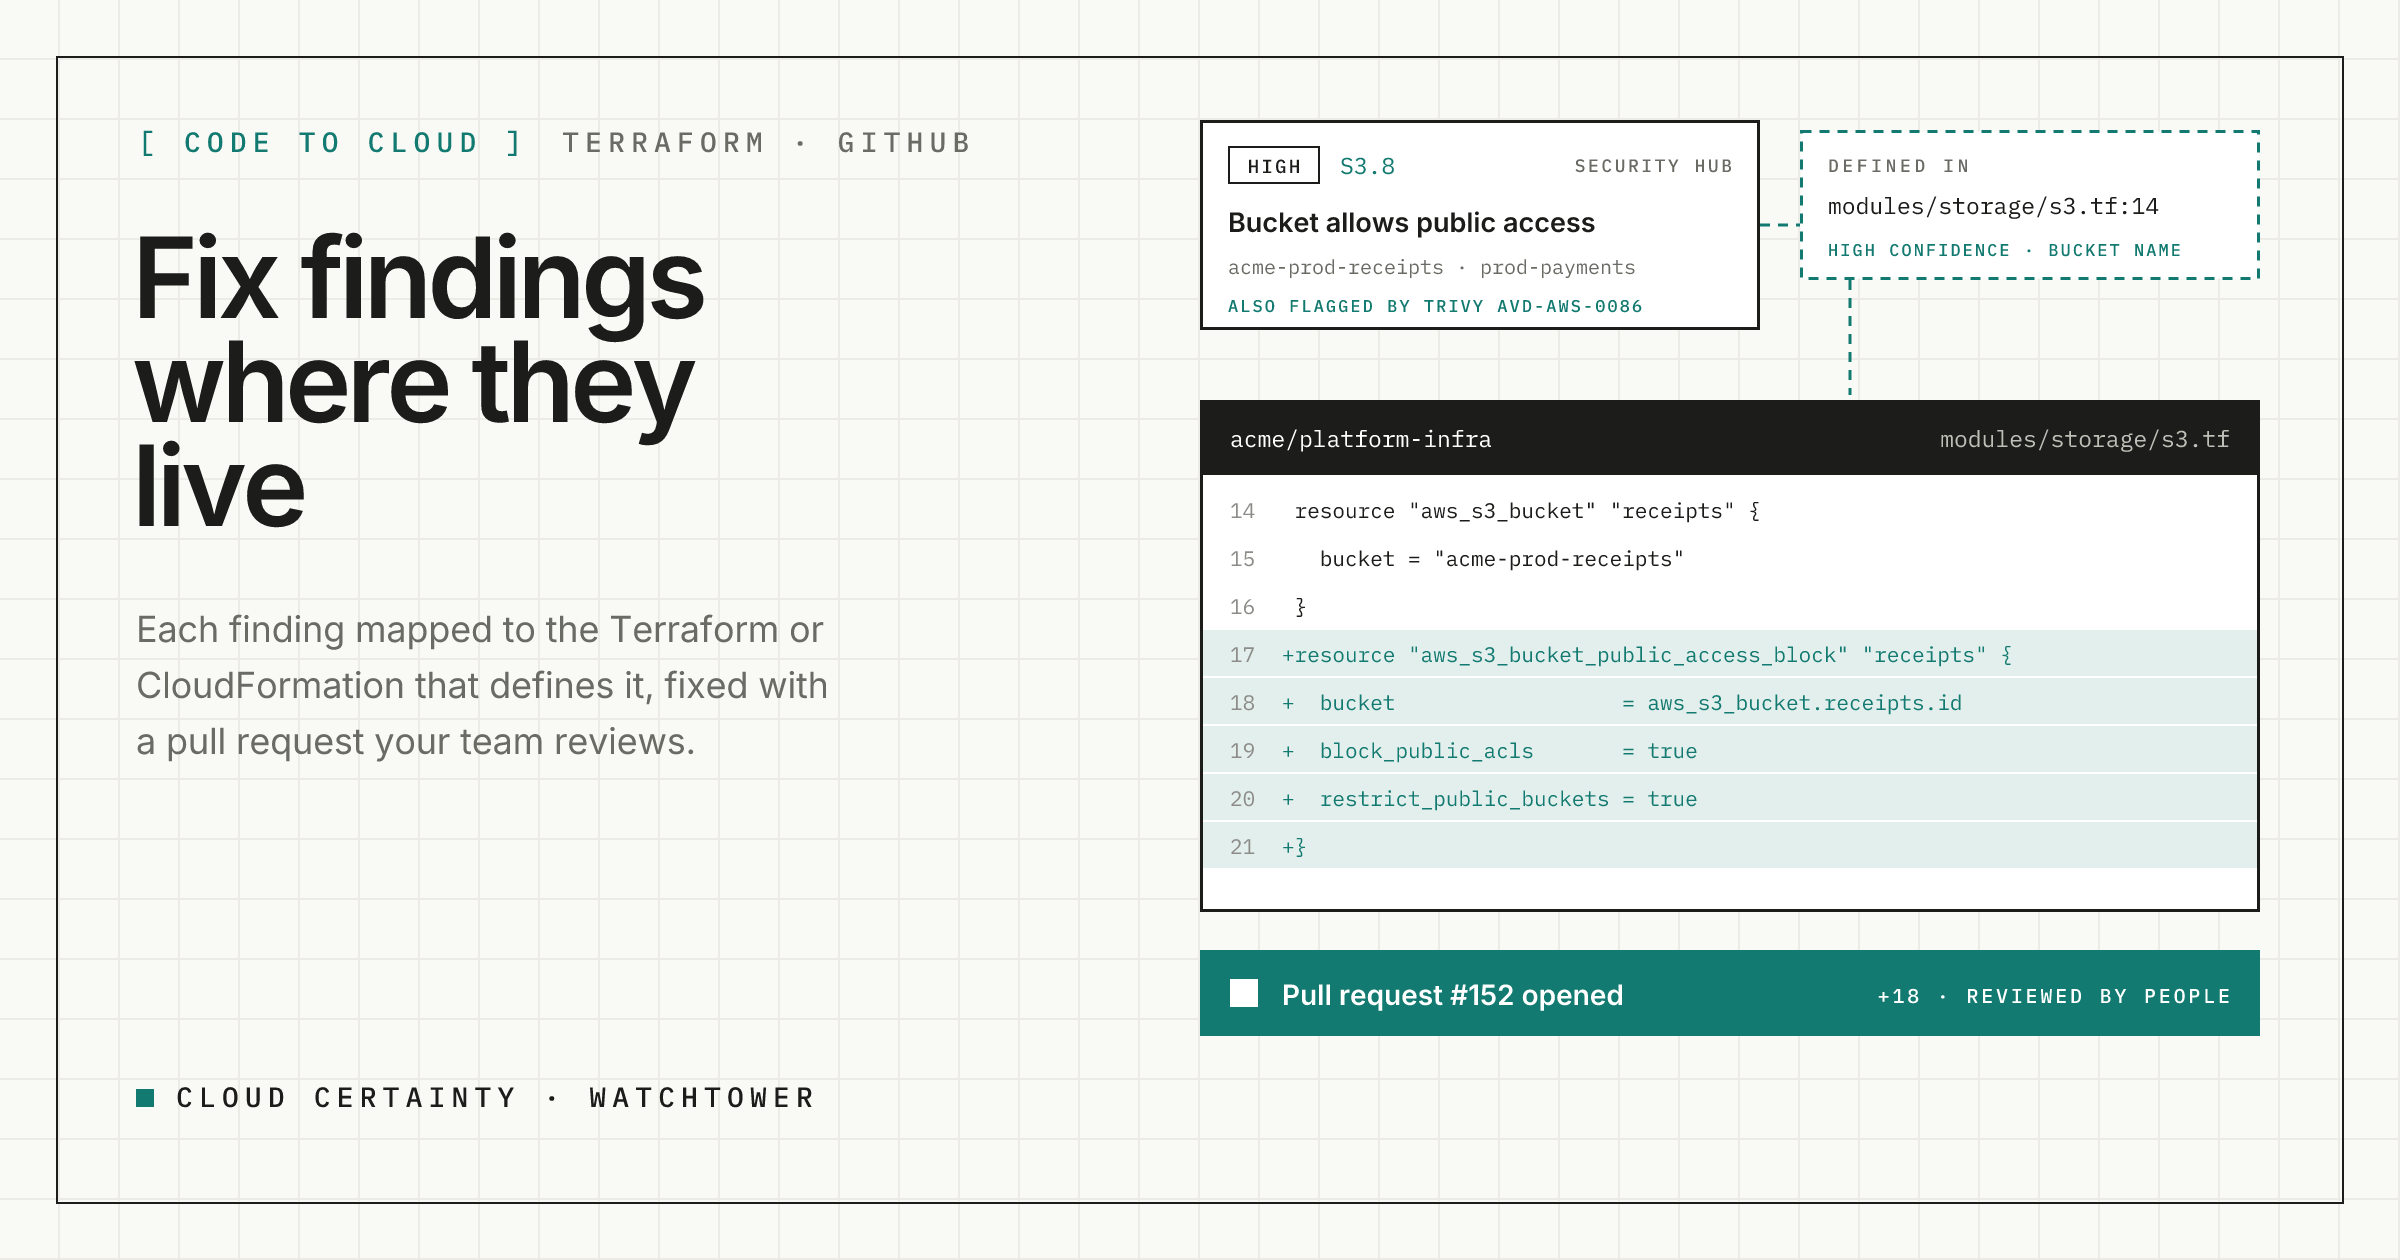
Fixing Security Hub findings where they live: in your Terraform and CloudFormation
A fix made in the AWS console is undone by the next terraform apply. Here is how Watchtower maps each finding to the code that defines the resource, opens a pull request with the fix, and brings Trivy, SonarCloud and SARIF findings into the same picture.
4 min read →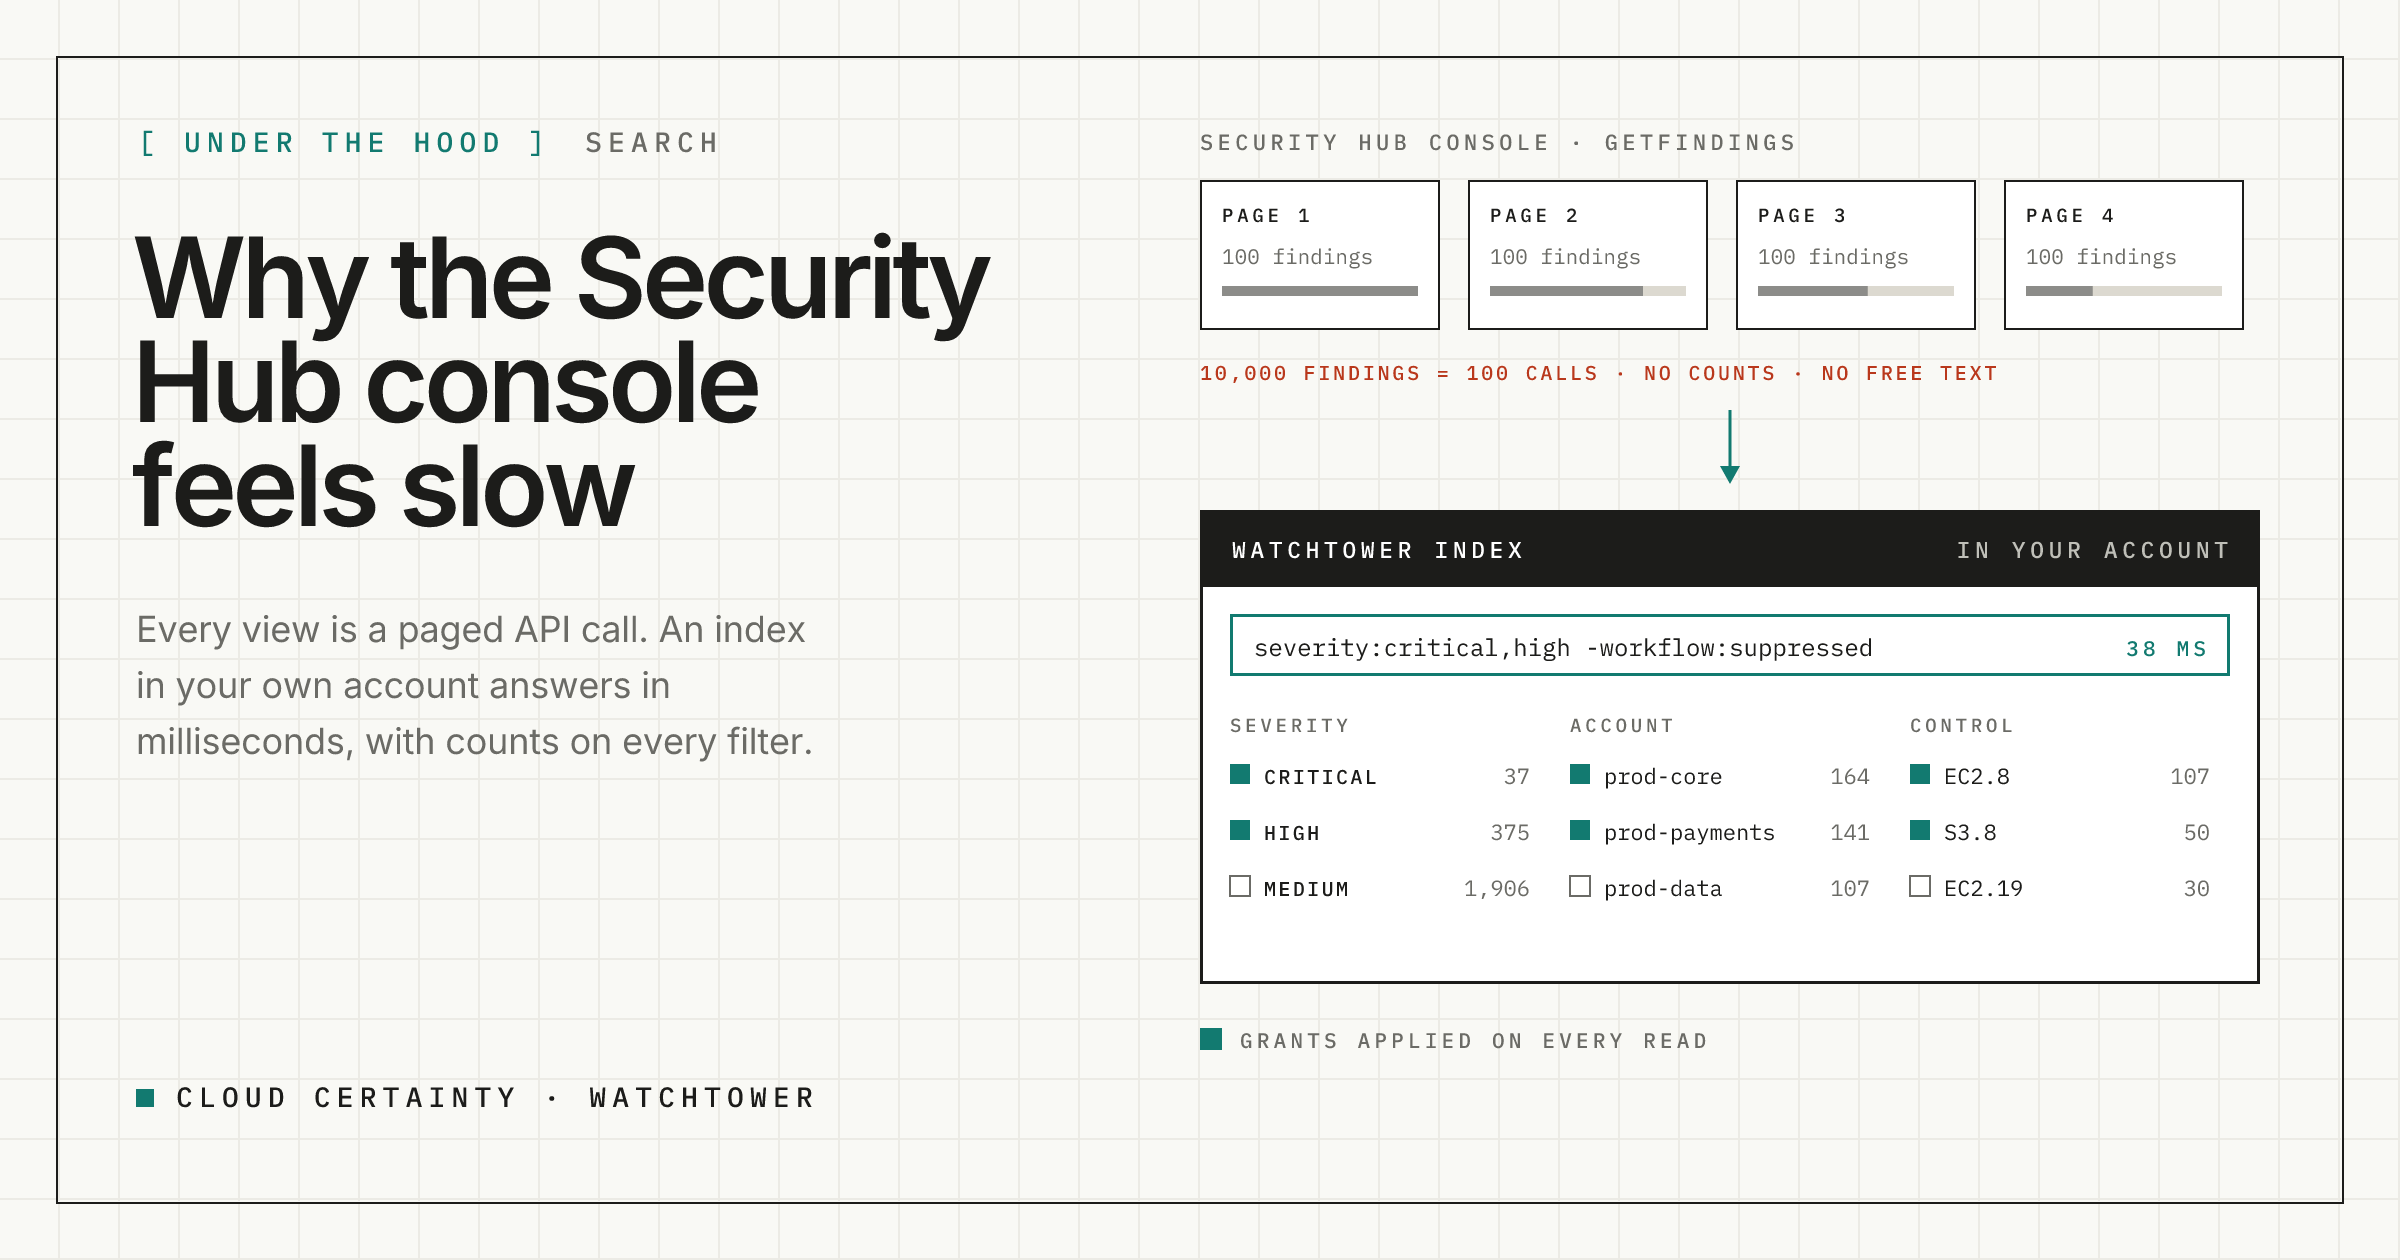
Why the Security Hub console feels slow, and how an index fixes it
Every view in the Security Hub console is a live, paged call to GetFindings. Here is why that rules out free text, counts and fast sorting, and how Watchtower keeps its own index without giving up live detail or AWS-enforced access.
4 min read →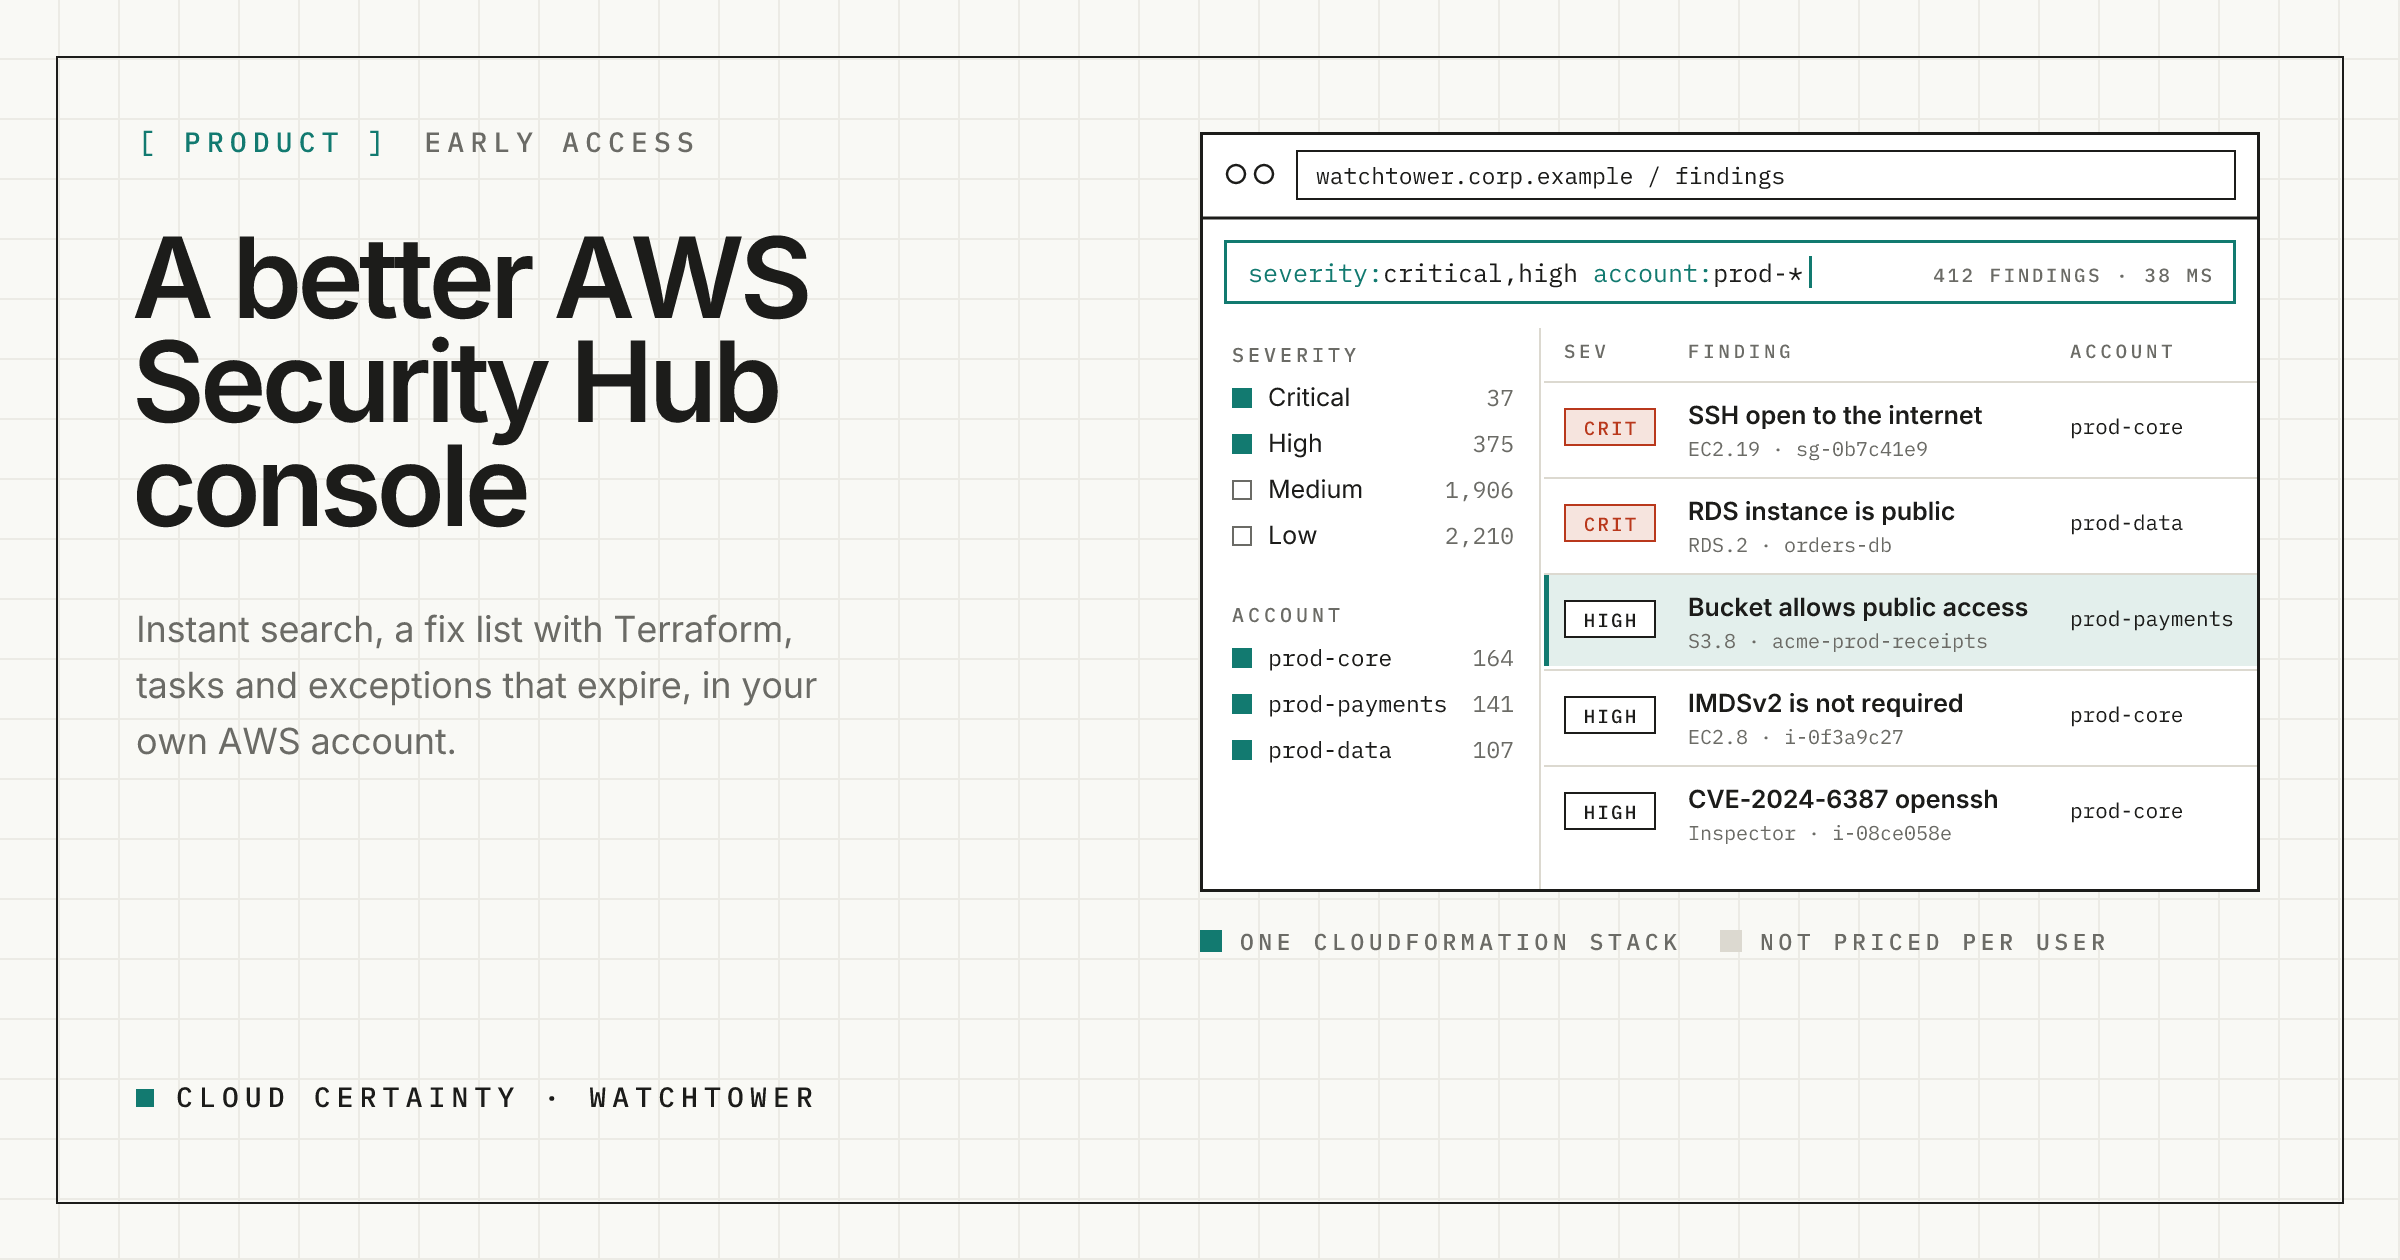
Watchtower: a better AWS Security Hub console, in your own AWS account
Security Hub collects findings from every account and Region, then leaves you with a slow list. Watchtower is a console that runs in your own AWS account and adds instant search, a fix list with Terraform and CloudFormation, tasks, expiring exceptions and links to your code.
4 min read →